Advanced API Integration and CAPTCHA Processing
Your scraper still gets obstructed. Since modern anti-bot systems don't rely on a single detection technique. This guide maps out every detection method sites utilize today, from standard to advanced.
Let's go through them all. "Host": "", "Connection": "keep-alive", "sec-ch-ua": '"Chromium"; v="121"', "sec-ch-ua-mobile": "?, 2, 2); const hash = canvas.toDataURL().
How to Bypass 2026 Automation Filters
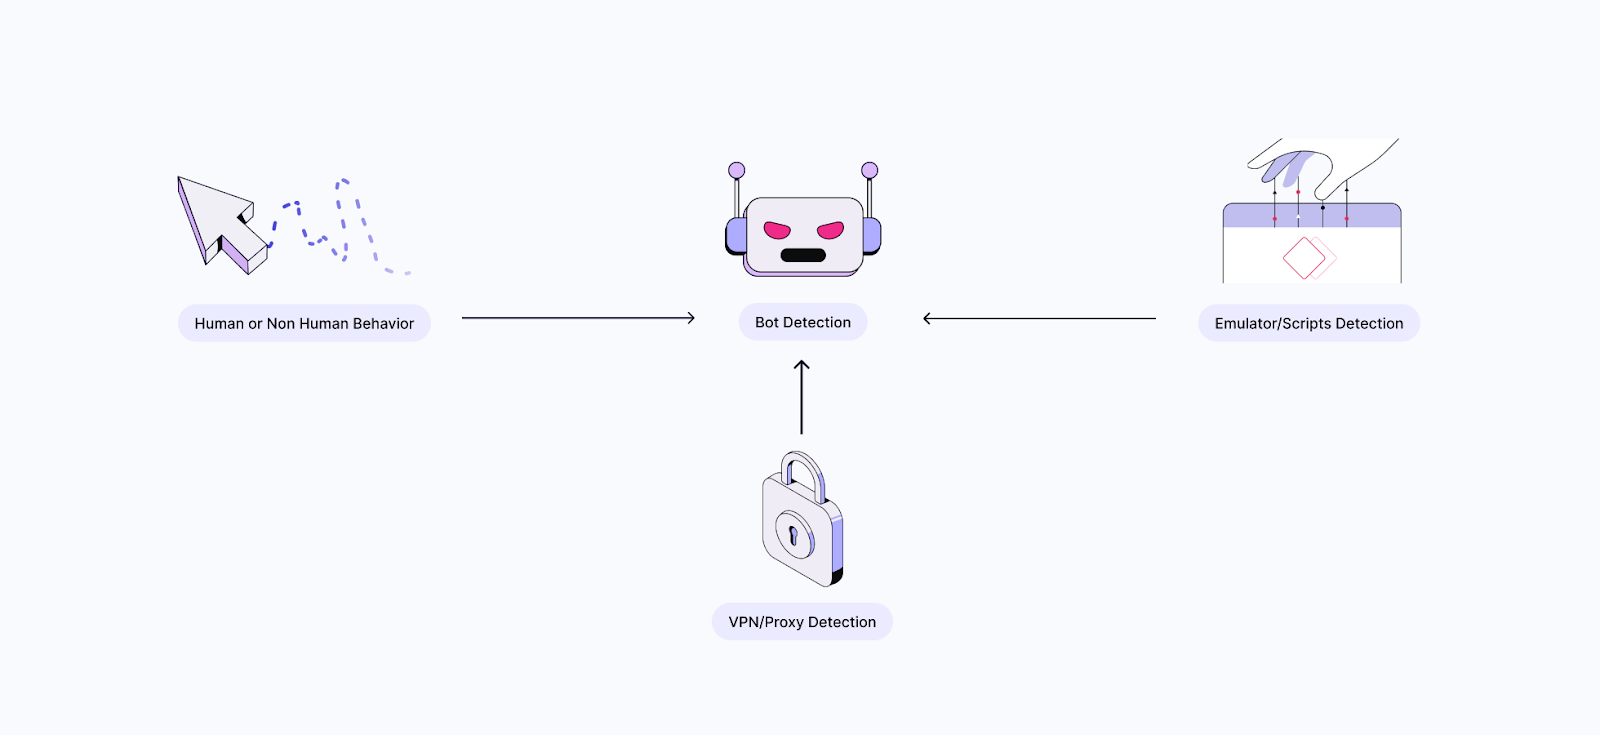
Many scrapers get obstructed at layers 3-4, not 5-7. fixing one layer while neglecting others won't work these catch 55% of bots before JS even runs however they're set off by undetectable signals mouse movement and timing matter more each year usage bot detection sites to audit your setup even best stealth can't prevent all difficulties For dealing with the CAPTCHA layer when it triggers, take a look at passxapi-python it supplies a unified API for reCAPTCHA, hCaptcha, Gate, and FunCaptcha, so you can focus on the other layers.
In this tutorial, you will discover the following: What Cloudflare is. A much deeper take a look at its WAF system. How its anti-bot system works from a technical perspective. What occurs when you target a Cloudflare-protected website utilizing basic automation tools. Top-level approaches to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
Xrumer softwareLet's dive in! Cloudflare is a web infrastructure and security business that operates among the biggest networks on the Web. It offers a thorough suite of services created to make sites quicker and more protected. At its core, Cloudflare functions primarily as a CDN (Material Shipment Network), caching website content on a worldwide network to enhance load times and reduce latency.
Advanced OCR Strategies in Automation Detection in 2026
By incorporating with Cloudflare's network, sites can quickly acquire improved security and enhanced performance. This can be enabled on any web page served through its international network.
More particularly, the Cloudflare WAF beings in front of your web applications. It examines and filters incoming demands in real time to stop attacks or undesirable traffic before they reach your servers or gain access to your web pages. As part of its multilayered defense technique, the Cloudflare WAF utilizes exclusive algorithms to discover and block harmful bots.
It looks at details like the cipher suites provided, the order of negotiation, and other low-level characteristics. Bots frequently reuse default or suspicious configurations that vary from those used by real internet browsers.
This includes the specific internet browser variation, running system, installed typefaces or extensions, and even subtle hardware attributes. These information points form a fingerprint that assists distinguish real users from automated scripts.: One of the strongest signs of automated traffic is abnormal habits. Cloudflare monitors patterns like rapid demands, absence of mouse motions, similar click paths, idle times, and more.
This is among the most complicated anti-bot strategies. Cloudflare usually supplies 2 modes of human verification: Constantly reveal the human verification challenge Automated human confirmation difficulty (only when suspicious activity is spotted) Check out both alternatives listed below! The very first mode is less common but uses stronger security. The idea is to always need human verification on the very first access to a site.
Xrumer softwareMastering Advanced Rotation and Network Automation
Try visiting it in incognito mode (to make sure a fresh session without any cookies), and you will see a CAPTCHA called Cloudflare Gate, even if you are a real human user:: By the time you read this short article, StackOverflow's bot defense may have changed or be working in a different way. In this case, if you are building an automated script, the only choice is to automate the Turnstile CAPTCHA interaction in a human-like way.
That is how it handles to confirm you are human with a single click. In this mode, Cloudflare only provides an obstacle if it believes a request might be from a bot. It does this by providing a JavaScript difficulty, which runs invisibly in the internet browser to validate that the client behaves like a legitimate user: This procedure is seamless and normally finishes instantly if you are a human utilizing a regular internet browser.
Since this causes minimal interruption for regular users, it is by far the most typical Cloudflare mode. If the JavaScript obstacle fails (meaning Cloudflare concludes the customer is likely to be a bot), it will escalate to revealing a Turnstile CAPTCHA for human confirmation: Now, you are back to what you saw in the previous circumstance.
Next-Gen Image Recognition and Security Solving
This page is protected by the Cloudflare WAF, so the automated JavaScript-based verification procedure will immediately begin. In the background, a series of POST demands are exchanged with Cloudflare's endpoints, transferring encrypted data within their payloads: The precise contents of these payloads are not openly documented.