Cybersecurity Trends and Expect for 2026
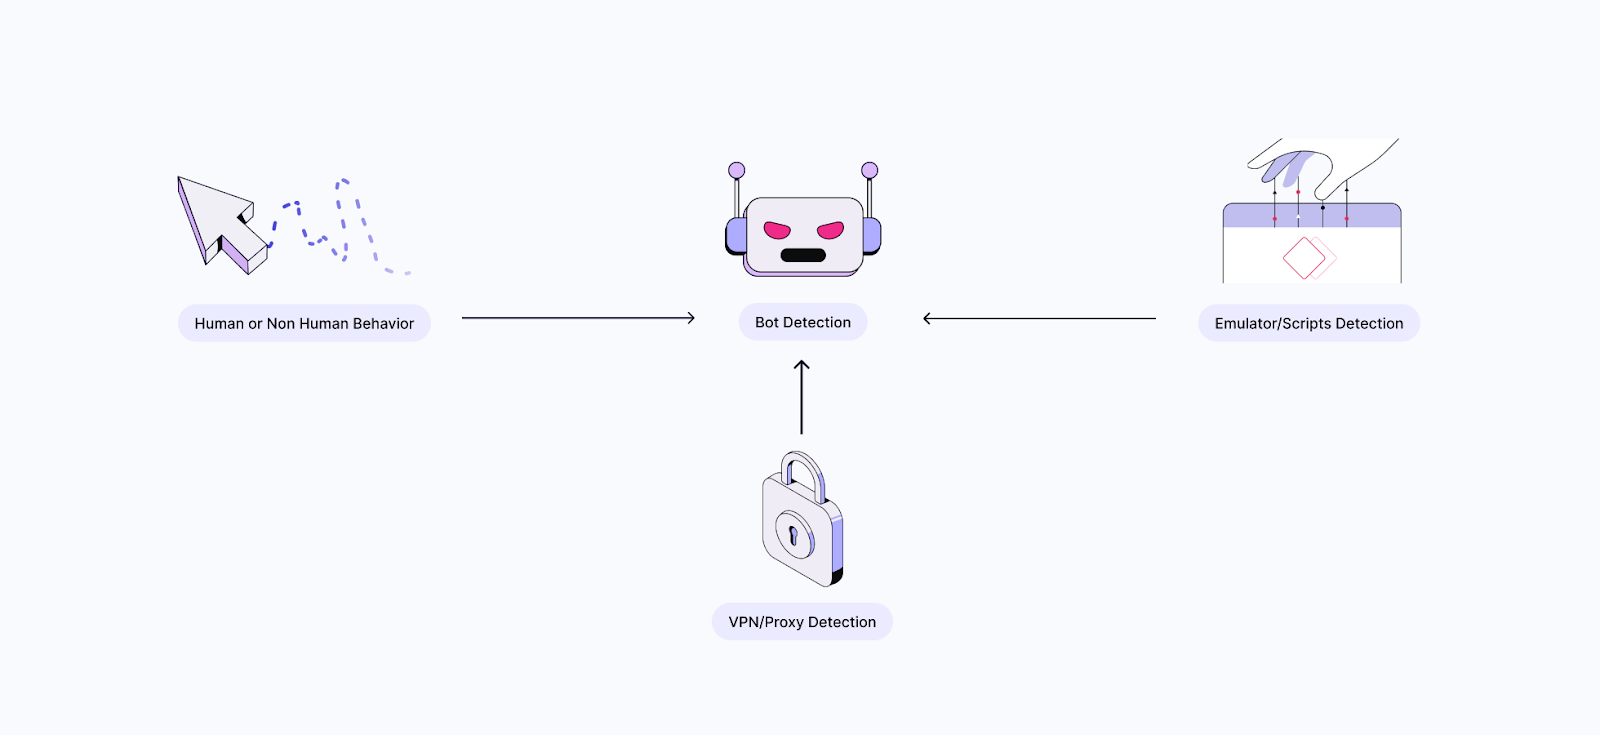
Most scrapers get obstructed at layers 3-4, not 5-7. repairing one layer while ignoring others will not work these catch 55% of bots before JS even runs however they're triggered by undetectable signals mouse movement and timing matter more each year usage bot detection websites to audit your setup even perfect stealth can't avoid all obstacles For managing the CAPTCHA layer when it triggers, have a look at passxapi-python it offers a unified API for reCAPTCHA, hCaptcha, Turnstile, and FunCaptcha, so you can focus on the other layers.
In this tutorial, you will learn the following: What Cloudflare is. A much deeper appearance at its WAF system. How its anti-bot system works from a technical viewpoint. What happens when you target a Cloudflare-protected website using basic automation tools. Top-level techniques to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
Let's dive in! Cloudflare is a web infrastructure and security business that runs one of the biggest networks on the Web. It uses a thorough suite of services developed to make websites quicker and more safe and secure. At its core, Cloudflare functions mostly as a CDN (Material Delivery Network), caching website material on an international network to improve load times and lower latency.
The Future of OCR and Security Resolution
By integrating with Cloudflare's network, websites can quickly acquire enhanced security and enhanced efficiency. This can be made it possible for on any web page served through its worldwide network.
More specifically, the Cloudflare WAF beings in front of your web applications. It inspects and filters incoming demands in real time to stop attacks or undesirable traffic before they reach your servers or gain access to your web pages. As part of its multilayered defense technique, the Cloudflare WAF utilizes proprietary algorithms to identify and obstruct malicious bots.
It looks at details like the cipher suites provided, the order of settlement, and other low-level traits. Bots and non-standard customers frequently have unusual, non-browser-like TLS signatures that provide away.: Takes a look at HTTP headers, cookies, user-agent strings, and other aspects. Bots typically recycle default or suspicious configurations that vary from those used by genuine browsers.
This includes the precise browser variation, running system, installed typefaces or extensions, and even subtle hardware qualities. These data points form a finger print that assists distinguish real users from automated scripts.: One of the strongest indicators of automated traffic is abnormal habits. Cloudflare monitors patterns like rapid demands, lack of mouse motions, identical click courses, idle times, and more.
XEvilAdvanced Bypass Techniques in Automation Detection for 2026
This is among the most complex anti-bot techniques. Cloudflare generally offers two modes of human confirmation: Constantly show the human confirmation obstacle Automated human verification challenge (only when suspicious activity is discovered) Check out both alternatives below! The very first mode is less typical but uses stronger protection. The idea is to always need human verification on the very first access to a site.
Attempt visiting it in incognito mode (to guarantee a fresh session with no cookies), and you will see a CAPTCHA called Cloudflare Turnstile, even if you are a genuine human user:: By the time you read this article, StackOverflow's bot defense may have changed or be working differently. In this case, if you are constructing an automated script, the only option is to automate the Turnstile CAPTCHA interaction in a human-like way.
XEvilIn this mode, Cloudflare just issues an obstacle if it thinks a demand might be from a bot., which runs invisibly in the internet browser to validate that the customer acts like a genuine user: This procedure is smooth and normally completes immediately if you are a human using a routine browser.
Because this triggers very little disruption for routine users, it is without a doubt the most common Cloudflare mode. Nevertheless, if the JavaScript obstacle fails (significance Cloudflare concludes the customer is most likely to be a bot), it will escalate to showing a Turnstile CAPTCHA for human verification: Now, you are back to what you saw in the previous scenario.
Still, if it does appear, you need a way to deal with it. Try opening the NopeCHA Cloudflare test page in incognito mode utilizing your web browser. This page is secured by the Cloudflare WAF, so the automated JavaScript-based verification process will instantly begin. In the background, a series of POST requests are exchanged with Cloudflare's endpoints, transferring encrypted data within their payloads: The exact contents of these payloads are not publicly recorded.