How AI Automation Impacts Digital Security
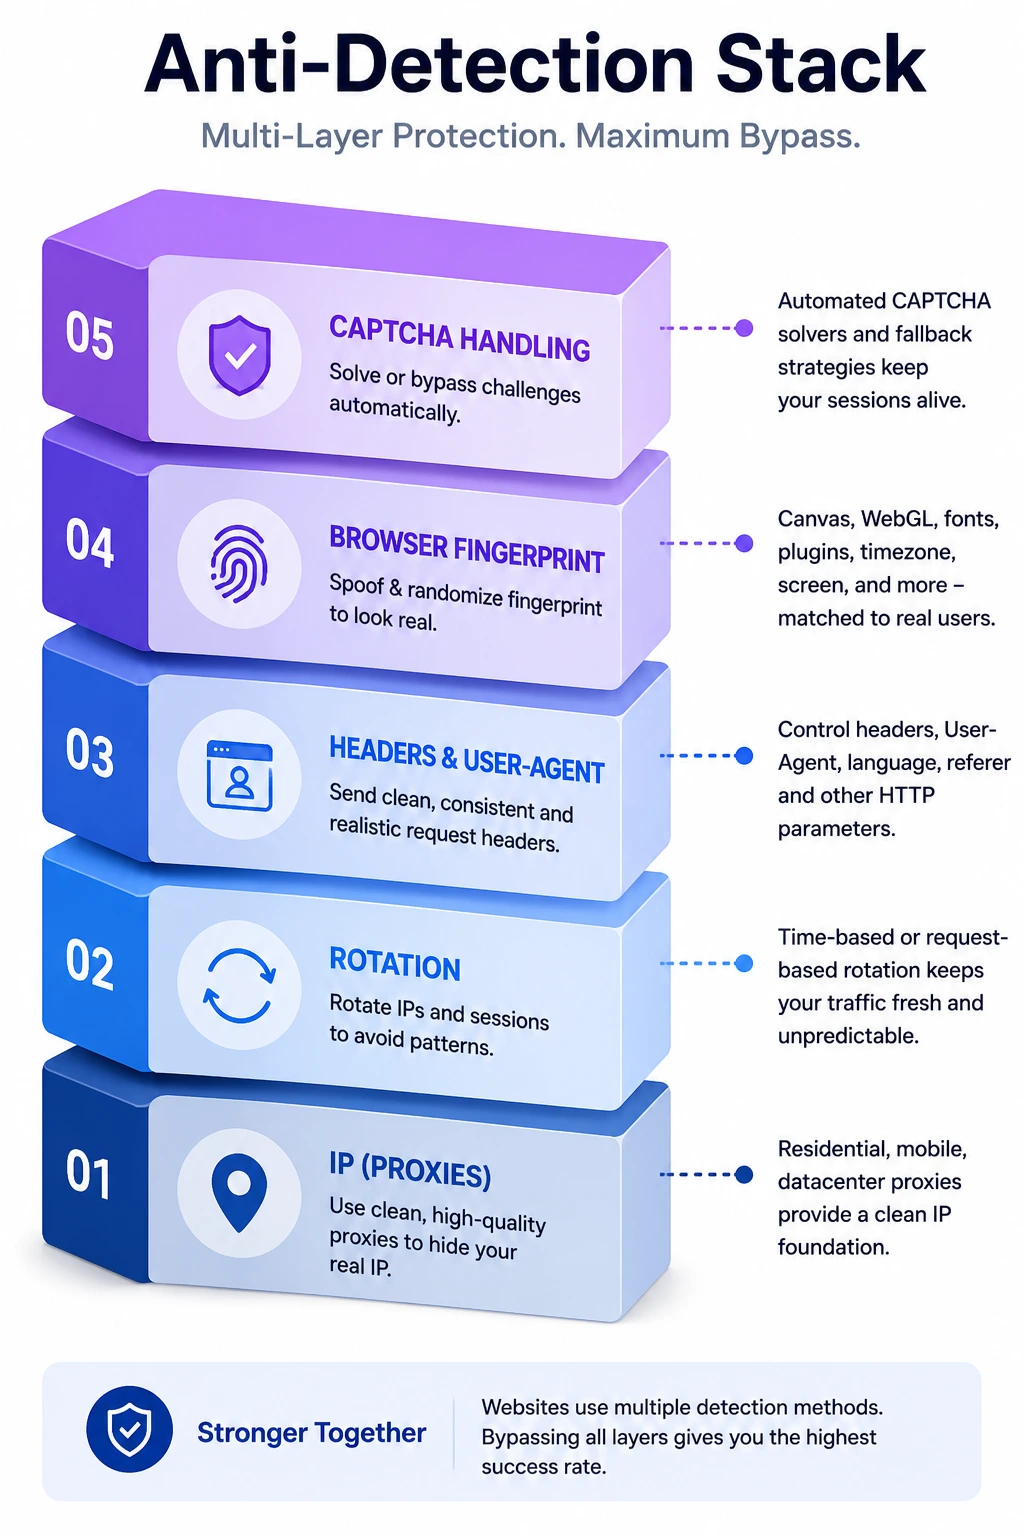
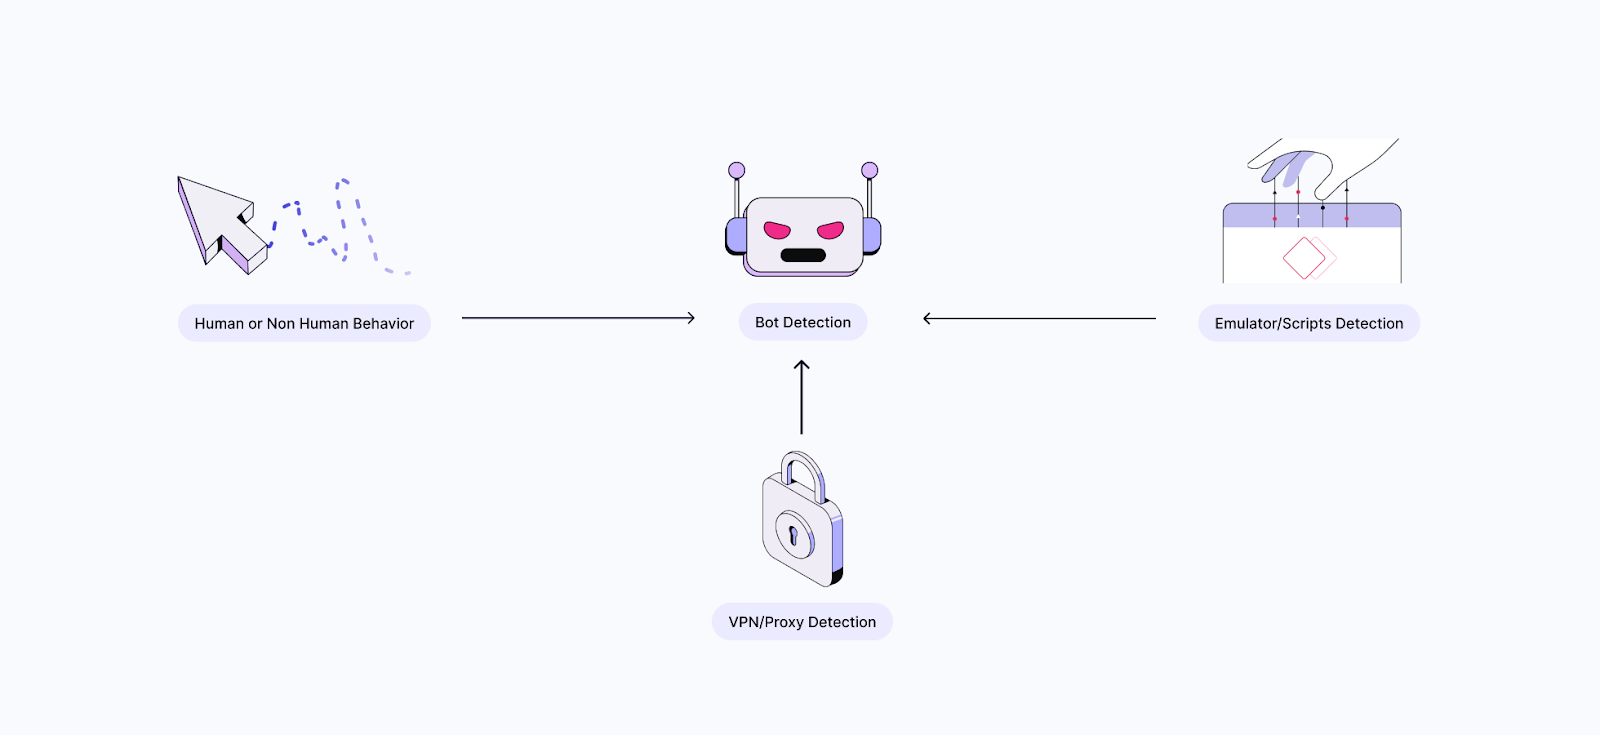
Your scraper still gets blocked. Due to the fact that contemporary anti-bot systems don't rely on a single detection approach. This guide maps out every detection strategy websites utilize today, from basic to advanced.
Let's go through them all. Anti-bot services maintain databases of recognized bad IPs: import httpx def check_ip_reputation(ip: str) -> dict: """Check if an IP is flagged in common databases.""" checks = # AbuseIPDB resp = ("", params= "ipAddress": ip, headers= "Secret": ABUSEIPDB_KEY ). json() checks [" abuse_score"] = resp [" information"] [" abuseConfidenceScore"] # Check if datacenter IP checks [" is_datacenter"] = is_datacenter_ip(ip) return checks def is_datacenter_ip(ip: str) -> bool: """Examine if IP belongs to a recognized hosting service provider.""" import ipaddress DATACENTER_RANGES = [" 13.0.0.0/ 8", # AWS "34.0.0.0/ 8", # GCP "40.0.0.0/ 8", # Azure "104.16.0.0/ 12", # Cloudflare "157.240.0.0/ 16", # Meta] addr = ipaddress.ip _ address(ip) return any( addr in ipaddress.ip _ network(cidr) for cidr in DATACENTER_RANGES) Enter fullscreen mode Exit fullscreen mode Use domestic proxies for delicate targets Turn IPs from different subnets Prevent datacenter IPs for websites with rigorous anti-bot Sites examine your IP's Autonomous System Number (ASN) to determine hosting providers: # What anti-bot services see: # AS7922 (Comcast) Residential # AS7018 (AT&T) Residential # AS16509 (Amazon/AWS) Datacenter # AS14061 (DigitalOcean) Datacenter # AS13335 (Cloudflare) CDN/VPN Enter fullscreen mode Exit fullscreen mode Every HTTP client has a distinct TLS handshake signature: # Different clients, various fingerprints: # Chrome 121: JA3 = 771,4865-4866-4867-49195 ...
curl: JA3 = 771,4865-4867-4866-49195 ... # Solution: curl_cffi mimics web browser TLS from curl_cffi import requests resp = ("", impersonate="chrome120") # Now your JA3 matches Chrome 120 precisely Enter fullscreen mode Exit fullscreen mode Browsers send out headers in a specific order. Python libraries don't: # Chrome sends out: # Host, Connection, sec-ch-ua, sec-ch-ua-mobile, # sec-ch-ua-platform, Upgrade-Insecure-Requests, # User-Agent, Accept, Sec-Fetch-Site ...
Fix: utilize OrderedDict or curl_cffi headers = "Host": "", "Connection": "keep-alive", "sec-ch-ua": '"Chromium"; v="121"', "sec-ch-ua-mobile": "? 0", "sec-ch-ua-platform": '"Windows"', "Upgrade-Insecure-Requests": "1", "User-Agent": "Mozilla/5.0 ...", "Accept": "text/html, ...", Get in fullscreen mode Exit fullscreen mode HTTP/2 settings (SETTINGS frame, WINDOW_UPDATE, CONCERN) likewise produce a distinct fingerprint: # Chrome's HTTP/2 settings: # HEADER_TABLE_SIZE: 65536 # MAX_CONCURRENT_STREAMS: 1000 # INITIAL_WINDOW_SIZE: 6291456 # MAX_HEADER_LIST_SIZE: 262144 # Python's default: various values # Detectable # curl_cffi handles this automatically # when you utilize impersonate="chrome120" Get in fullscreen mode Exit fullscreen mode Websites render hidden canvas elements and hash the outcome:// What anti-bot JS does: const canvas = document.createElement('canvas'); const ctx = canvas.getContext('2d'); ctx.textBaseline="top";="14px Arial"; ctx.fillText("Hey there, world!", 2, 2); const hash = canvas.toDataURL(). hashCode();// Various GPUs/drivers = different hash Go into fullscreen mode Exit fullscreen mode const gl = canvas.getContext('webgl'); const debugInfo = gl.getExtension( 'WEBGL_debug_renderer_info' );// Genuine internet browser: gl.getParameter(debugInfo.
Mastering Advanced Rotation and Web Privacy
A lot of scrapers get blocked at layers 3-4, not 5-7. repairing one layer while ignoring others won't work these catch 55% of bots before JS even runs however they're triggered by unnoticeable signals mouse motion and timing matter more each year usage bot detection sites to investigate your setup even ideal stealth can't prevent all challenges For dealing with the CAPTCHA layer when it activates, take a look at passxapi-python it offers a unified API for reCAPTCHA, hCaptcha, Gate, and FunCaptcha, so you can concentrate on the other layers.
In this tutorial, you will discover the following: What Cloudflare is. High-level approaches to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
Let's dive in! Cloudflare is a web infrastructure and security company that operates one of the biggest networks on the internet. It offers a comprehensive suite of services developed to make sites quicker and more secure. At its core, Cloudflare functions mainly as a CDN (Material Shipment Network), caching website material on a global network to improve load times and minimize latency.
Choosing the Dedicated Proxy Hosting for 2026
By integrating with Cloudflare's network, websites can quickly get enhanced security and optimized efficiency. This can be made it possible for on any web page served through its international network.
More specifically, the Cloudflare WAF sits in front of your web applications. It examines and filters inbound demands in real time to stop attacks or unwanted traffic before they reach your servers or access your web pages. As part of its multilayered defense technique, the Cloudflare WAF utilizes proprietary algorithms to identify and block malicious bots.
It looks at details like the cipher suites provided, the order of settlement, and other low-level qualities. Bots often reuse default or suspicious configurations that vary from those used by genuine web browsers.
This consists of the precise browser variation, running system, installed font styles or extensions, and even subtle hardware qualities. These data points form a fingerprint that helps differentiate genuine users from automated scripts.: One of the strongest indications of automated traffic is unnatural habits. Cloudflare screens patterns like fast demands, lack of mouse movements, similar click courses, idle times, and more.
This is among the most intricate anti-bot methods. Cloudflare generally offers two modes of human confirmation: Always reveal the human confirmation difficulty Automated human confirmation difficulty (just when suspicious activity is spotted) Explore both alternatives below! The first mode is less common however offers more powerful defense. The concept is to constantly require human confirmation on the first access to a site.
Strategies for Expand Network Infrastructure with Automation
Try visiting it in incognito mode (to guarantee a fresh session with no cookies), and you will see a CAPTCHA called Cloudflare Turnstile, even if you are a genuine human user:: By the time you read this short article, StackOverflow's bot security may have changed or be working differently. In this case, if you are building an automated script, the only choice is to automate the Turnstile CAPTCHA interaction in a human-like method.
That is how it handles to validate you are human with a single click. In this mode, Cloudflare just issues a challenge if it thinks a demand may be from a bot. It does this by presenting a JavaScript difficulty, which runs invisibly in the internet browser to validate that the client behaves like a genuine user: This procedure is seamless and usually finishes instantly if you are a human using a routine browser.
Considering that this triggers minimal interruption for regular users, it is without a doubt the most common Cloudflare mode. If the JavaScript challenge stops working (meaning Cloudflare concludes the client is likely to be a bot), it will escalate to revealing a Turnstile CAPTCHA for human verification: Now, you are back to what you saw in the previous situation.
Advanced API Solutions and CAPTCHA Solving
Still, if it does appear, you need a method to deal with it. Attempt opening the NopeCHA Cloudflare test page in incognito mode utilizing your internet browser. This page is secured by the Cloudflare WAF, so the automated JavaScript-based confirmation procedure will right away start. In the background, a series of POST requests are exchanged with Cloudflare's endpoints, transmitting encrypted data within their payloads: The exact contents of these payloads are not publicly recorded.