Methods to Scale Network Resources with Automation

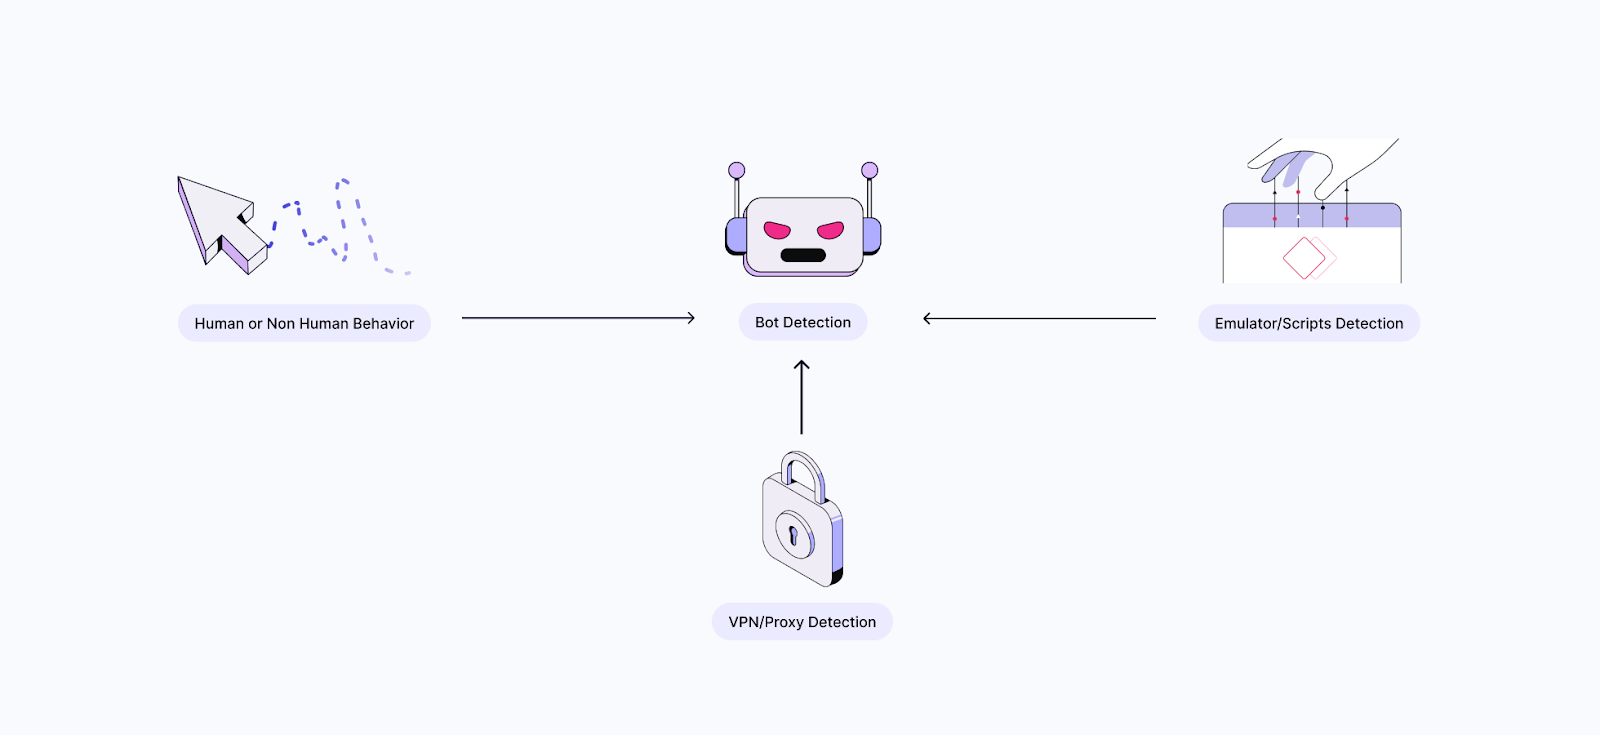
You've handled CAPTCHAs, rotated proxies, and spoofed your User-Agent. Your scraper still gets blocked. Why? Due to the fact that modern anti-bot systems do not depend on a single detection method. They stack multiple layers and you require to comprehend all of them to build a scraper that survives in production. This guide draws up every detection method sites use today, from fundamental to advanced.
Let's go through them all. Anti-bot services preserve databases of recognized bad IPs: import httpx def check_ip_reputation(ip: str) -> dict: """Check if an IP is flagged in common databases.""" checks = # AbuseIPDB resp = ("", params= "ipAddress": ip, headers= "Key": ABUSEIPDB_KEY ). json() checks [" abuse_score"] = resp [" information"] [" abuseConfidenceScore"] # Examine if datacenter IP checks [" is_datacenter"] = is_datacenter_ip(ip) return checks def is_datacenter_ip(ip: str) -> bool: """Inspect if IP belongs to a known hosting company.""" import ipaddress DATACENTER_RANGES = [" 13.0.0.0/ 8", # AWS "34.0.0.0/ 8", # GCP "40.0.0.0/ 8", # Azure "104.16.0.0/ 12", # Cloudflare "157.240.0.0/ 16", # Meta] addr = ipaddress.ip _ address(ip) return any( addr in ipaddress.ip _ network(cidr) for cidr in DATACENTER_RANGES) Enter fullscreen mode Exit fullscreen mode Use domestic proxies for delicate targets Turn IPs from different subnets Avoid datacenter IPs for websites with rigorous anti-bot Websites inspect your IP's Autonomous System Number (ASN) to recognize hosting suppliers: # What anti-bot services see: # AS7922 (Comcast) Residential # AS7018 (AT&T) Residential # AS16509 (Amazon/AWS) Datacenter # AS14061 (DigitalOcean) Datacenter # AS13335 (Cloudflare) CDN/VPN Go into fullscreen mode Exit fullscreen mode Every HTTP client has a special TLS handshake signature: # Various clients, different fingerprints: # Chrome 121: JA3 = 771,4865-4866-4867-49195 ...
curl: JA3 = 771,4865-4867-4866-49195 ... # Solution: curl_cffi mimics browser TLS from curl_cffi import demands resp = ("", impersonate="chrome120") # Now your JA3 matches Chrome 120 precisely Get in fullscreen mode Exit fullscreen mode Web browsers send headers in a specific order. Python libraries do not: # Chrome sends: # Host, Connection, sec-ch-ua, sec-ch-ua-mobile, # sec-ch-ua-platform, Upgrade-Insecure-Requests, # User-Agent, Accept, Sec-Fetch-Site ...
Repair: use OrderedDict or curl_cffi headers = "Host": "", "Connection": "keep-alive", "sec-ch-ua": '"Chromium"; v="121"', "sec-ch-ua-mobile": "? 0", "sec-ch-ua-platform": '"Windows"', "Upgrade-Insecure-Requests": "1", "User-Agent": "Mozilla/5.0 ...", "Accept": "text/html, ...", Go into fullscreen mode Exit fullscreen mode HTTP/2 settings (SETTINGS frame, WINDOW_UPDATE, PRIORITY) also produce a distinct finger print: # Chrome's HTTP/2 settings: # HEADER_TABLE_SIZE: 65536 # MAX_CONCURRENT_STREAMS: 1000 # INITIAL_WINDOW_SIZE: 6291456 # MAX_HEADER_LIST_SIZE: 262144 # Python's default: different worths # Noticeable # curl_cffi handles this immediately # when you use impersonate="chrome120" Enter fullscreen mode Exit fullscreen mode Sites render hidden canvas components and hash the outcome:// What anti-bot JS does: const canvas = document.createElement('canvas'); const ctx = canvas.getContext('2d'); ctx.textBaseline="leading";="14px Arial"; ctx.fillText("Hello, world!", 2, 2); const hash = canvas.toDataURL(). hashCode();// Different GPUs/drivers = various hash Get in fullscreen mode Exit fullscreen mode const gl = canvas.getContext('webgl'); const debugInfo = gl.getExtension( 'WEBGL_debug_renderer_info' );// Genuine internet browser: gl.getParameter(debugInfo.
How AI Automation Affects Network Security
A lot of scrapers get blocked at layers 3-4, not 5-7. fixing one layer while disregarding others will not work these catch 55% of bots before JS even runs but they're set off by invisible signals mouse motion and timing matter more each year use bot detection sites to investigate your setup even best stealth can't avoid all obstacles For dealing with the CAPTCHA layer when it activates, take a look at passxapi-python it provides a unified API for reCAPTCHA, hCaptcha, Gate, and FunCaptcha, so you can focus on the other layers.
In this tutorial, you will discover the following: What Cloudflare is. A much deeper take a look at its WAF mechanism. How its anti-bot system works from a technical perspective. What takes place when you target a Cloudflare-protected website using standard automation tools. Top-level techniques to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
XEvil 6 Beta setupLet's dive in! Cloudflare is a web infrastructure and security company that runs one of the largest networks on the internet. It offers a thorough suite of services created to make websites much faster and more secure. At its core, Cloudflare functions primarily as a CDN (Material Delivery Network), caching site material on an international network to enhance load times and decrease latency.
Cybersecurity Predictions to Expect for 2026
By integrating with Cloudflare's network, websites can quickly get enhanced security and optimized efficiency. This has actually made Cloudflare the go-to service for countless websites worldwide. Among the reasons Cloudflare is so popular is its WAF (Web Application Firewall Software). This can be made it possible for on any web page served through its worldwide network.
More specifically, the Cloudflare WAF beings in front of your web applications. It examines and filters inbound demands in genuine time to stop attacks or undesirable traffic before they reach your servers or access your web pages. As part of its multilayered defense technique, the Cloudflare WAF utilizes exclusive algorithms to discover and block destructive bots.
It looks at details like the cipher suites provided, the order of settlement, and other low-level traits. Bots frequently recycle default or suspicious configurations that vary from those used by real browsers.
This includes the precise web browser version, operating system, set up typefaces or extensions, and even subtle hardware qualities. These information points form a fingerprint that helps differentiate genuine users from automated scripts.: One of the greatest indicators of automated traffic is unnatural behavior. Cloudflare displays patterns like rapid requests, lack of mouse movements, identical click courses, idle times, and more.
Cloudflare usually provides two modes of human verification: Constantly reveal the human confirmation difficulty Automated human confirmation difficulty (just when suspicious activity is spotted) Check out both alternatives below! The concept is to constantly require human verification on the first access to a site.
XEvil 6 Beta setup
Cybersecurity Trends and Expect for 2026
Try visiting it in incognito mode (to ensure a fresh session without any cookies), and you will see a CAPTCHA called Cloudflare Gate, even if you are a genuine human user:: By the time you read this short article, StackOverflow's bot defense might have changed or be working differently. In this case, if you are building an automated script, the only choice is to automate the Turnstile CAPTCHA interaction in a human-like way.
That is how it handles to confirm you are human with a single click. In this mode, Cloudflare just issues a difficulty if it presumes a request may be from a bot. It does this by providing a JavaScript challenge, which runs invisibly in the internet browser to validate that the customer acts like a legitimate user: This process is seamless and normally completes instantly if you are a human using a routine internet browser.
Considering that this causes very little disruption for routine users, it is without a doubt the most typical Cloudflare mode. If the JavaScript difficulty fails (significance Cloudflare concludes the client is likely to be a bot), it will escalate to showing a Gate CAPTCHA for human verification: Now, you are back to what you saw in the previous scenario.
Smart Identity Management Workflows in 2026
This page is safeguarded by the Cloudflare WAF, so the automated JavaScript-based verification procedure will immediately start. In the background, a series of POST demands are exchanged with Cloudflare's endpoints, transferring encrypted information within their payloads: The exact contents of these payloads are not publicly recorded.