Scaling Network Workloads with Enterprise Automation
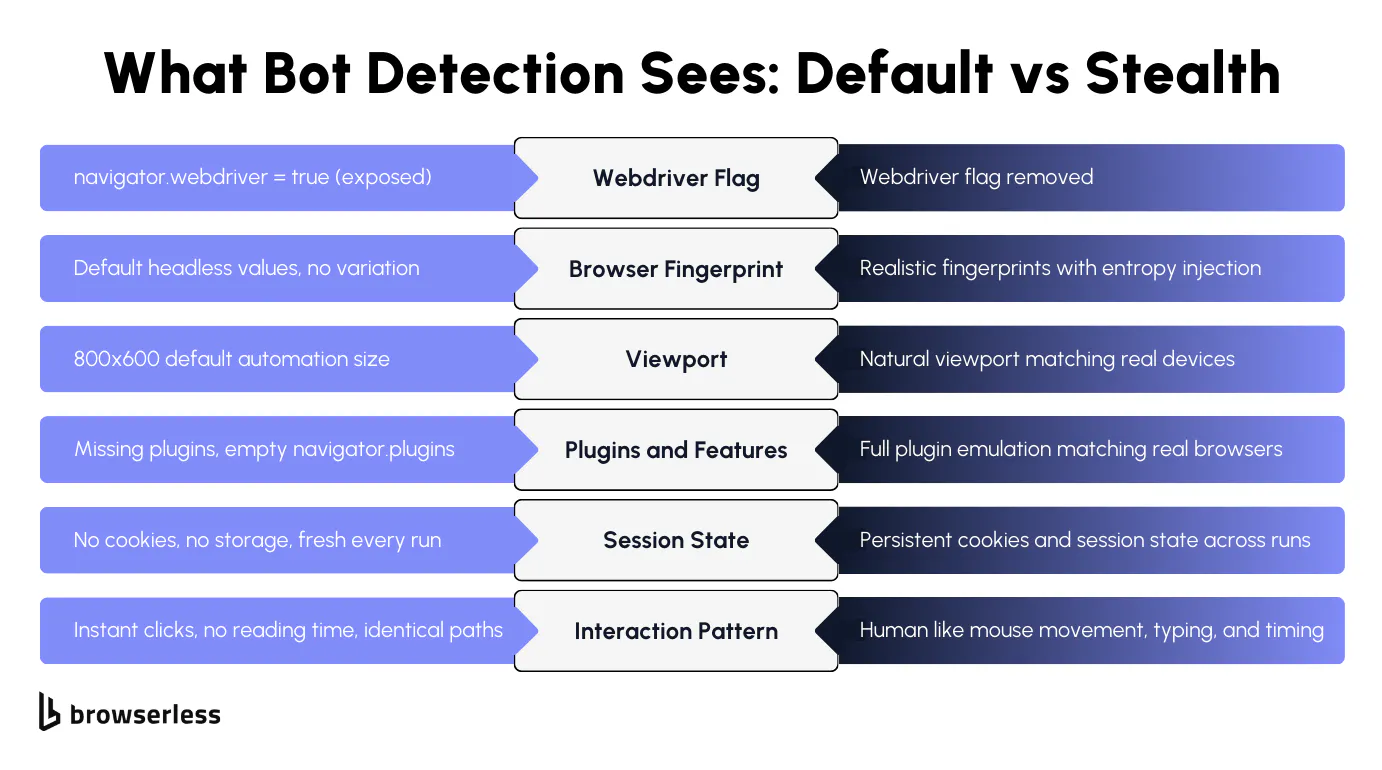
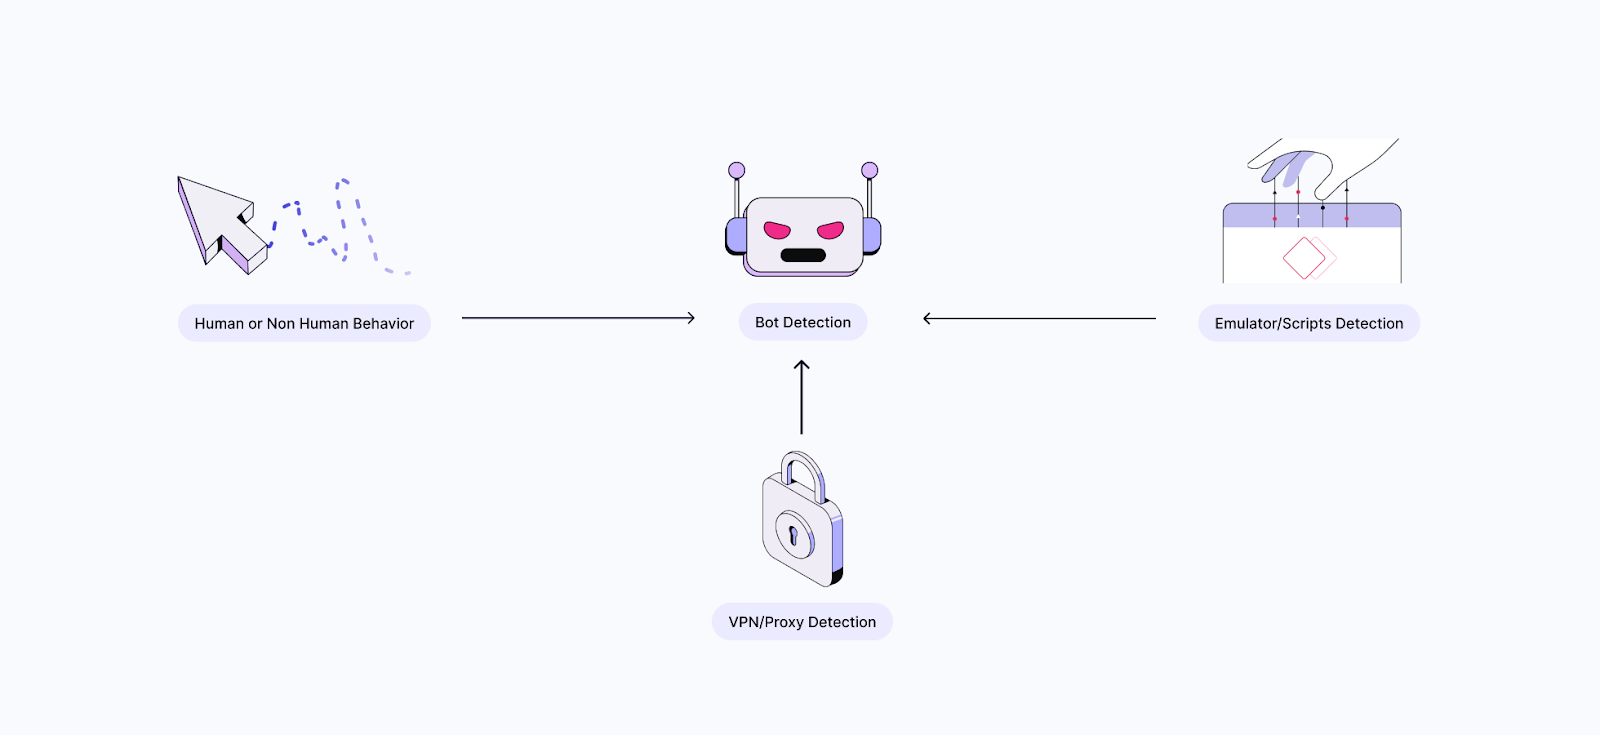
The majority of scrapers get obstructed at layers 3-4, not 5-7. repairing one layer while ignoring others won't work these catch 55% of bots before JS even runs however they're set off by invisible signals mouse motion and timing matter more each year use bot detection websites to investigate your setup even ideal stealth can't prevent all obstacles For managing the CAPTCHA layer when it activates, have a look at passxapi-python it offers a unified API for reCAPTCHA, hCaptcha, Gate, and FunCaptcha, so you can concentrate on the other layers.
In this tutorial, you will find out the following: What Cloudflare is. A much deeper take a look at its WAF mechanism. How its anti-bot system works from a technical point of view. What occurs when you target a Cloudflare-protected website utilizing basic automation tools. High-level methods to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
It uses a detailed suite of services developed to make sites faster and more safe and secure., caching website material on a worldwide network to enhance load times and reduce latency.
Understanding IP Rotation and Web Privacy
By integrating with Cloudflare's network, websites can quickly acquire enhanced security and enhanced performance. This can be enabled on any web page served through its international network.
More specifically, the Cloudflare WAF sits in front of your web applications. It examines and filters incoming requests in real time to stop attacks or undesirable traffic before they reach your servers or gain access to your websites. As part of its multilayered defense technique, the Cloudflare WAF uses exclusive algorithms to spot and obstruct harmful bots.
It looks at information like the cipher suites provided, the order of negotiation, and other low-level characteristics. Bots typically reuse default or suspicious setups that differ from those used by genuine web browsers.
This includes the specific web browser variation, running system, set up typefaces or extensions, and even subtle hardware characteristics. These information points form a finger print that assists differentiate genuine users from automated scripts.: Among the strongest indications of automated traffic is abnormal habits. Cloudflare screens patterns like quick demands, lack of mouse movements, similar click courses, idle times, and more.
XEvil 6 Beta standaloneThe Future of OCR and CAPTCHA Solving
This is among the most complicated anti-bot methods. Cloudflare typically supplies 2 modes of human confirmation: Constantly reveal the human verification challenge Automated human verification challenge (just when suspicious activity is detected) Explore both choices below! The first mode is less typical but uses stronger protection. The concept is to constantly need human confirmation on the first access to a website.
Attempt visiting it in incognito mode (to make sure a fresh session with no cookies), and you will see a CAPTCHA called Cloudflare Turnstile, even if you are a real human user:: By the time you read this article, StackOverflow's bot security may have changed or be working differently. In this case, if you are developing an automated script, the only alternative is to automate the Turnstile CAPTCHA interaction in a human-like way.
XEvil V5That is how it manages to validate you are human with a single click. In this mode, Cloudflare just issues a challenge if it suspects a demand might be from a bot. It does this by providing a JavaScript challenge, which runs invisibly in the web browser to verify that the customer behaves like a legitimate user: This procedure is smooth and normally finishes immediately if you are a human using a regular browser.
Considering that this triggers very little disruption for routine users, it is by far the most common Cloudflare mode. However, if the JavaScript obstacle fails (significance Cloudflare concludes the client is most likely to be a bot), it will intensify to showing a Gate CAPTCHA for human confirmation: Now, you are back to what you saw in the previous scenario.
This page is secured by the Cloudflare WAF, so the automated JavaScript-based confirmation procedure will instantly begin. In the background, a series of POST demands are exchanged with Cloudflare's endpoints, transmitting encrypted data within their payloads: The specific contents of these payloads are not publicly documented.