The Complete Guide to Captcha Automation Fundamentals

IAM automation combines identity management, getting rid of redundant gain access to protocols to streamline user oversight, decrease threat direct exposure, and boost efficiency. It minimizes sprawl by enhancing application access and decreasing overall costs. Automated IAM faces difficulties such as managing access sprawl, incorporating different applications, making sure protected employee lifecycle management, and keeping easy to use identity governance across various systems.
Execute a centralized identity platform that simplifies employee lifecycle actions, combines gain access to throughout applications, and minimizes manual errors. Standardize policies, use vibrant role assignments, and screen usage with robust analytics for enhanced performance and security.
A creator went to sleep with a healthy service and got up to find that AI-generated code had cancelled every active subscription in his business. This occurred immediately, while he slept. The clients never ever asked to leave. An automated ...
This article presents services that allow you to: Connect identities with your system of record Synchronize identities in between Active Directory site Domain Services (AD DS) and Microsoft Entra ID Automate provisioning of users into non-Microsoft applications In a lot of designs, the human resources (HR) system is the source-of-authority for recently developed digital identities.
Implementing Dedicated Infrastructure Leasing
If a new user joins a company, they have a record in the HR system. That user likely needs an account to gain access to Microsoft 365 services such as Teams and SharePoint, or non-Microsoft applications., into Microsoft Entra ID directly, or into AD DS.
To develop a complete user profile for a worker identity, companies often merge info from several HR systems, databases, and other user information stores. MIM supplies an abundant set of adapters and integration services interoperating with heterogeneous platforms both on-premises and in the cloud. MIM provides guideline extension and workflow abilities features for advanced situations requiring information change and debt consolidation from numerous sources.
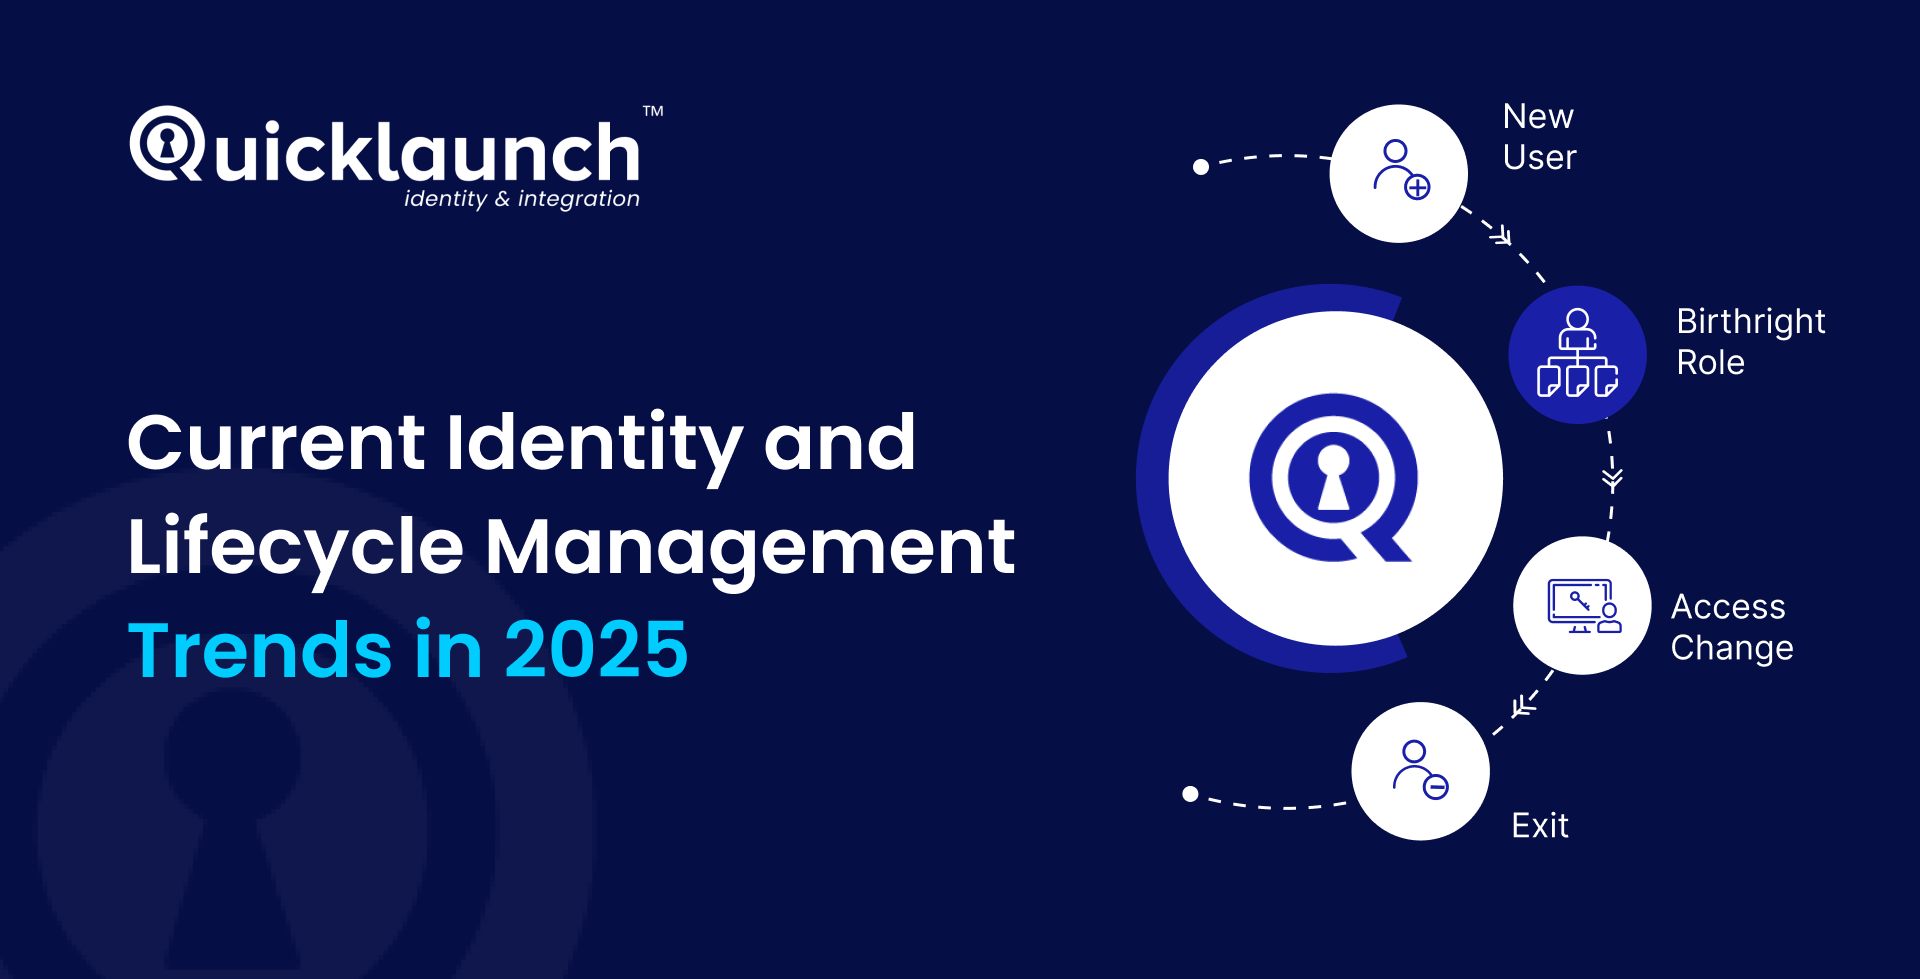
The identity can be provisioned into downstream systems such as advertisement DS. As consumers move applications to the cloud, and integrate with Microsoft Entra ID, users frequently need accounts in Microsoft Entra ID, and Microsoft Windows Server Active Directory site to access the applications for their work. Here are 5 common scenarios in which items need to be synchronized between Microsoft Windows Server Active Directory and Microsoft Entra ID.
Utilize the table following the situations to determine what technical solution provides the synchronization. Use the numbered areas in the next 2 area to cross recommendation the following table. For users in Microsoft Windows Server Active Directory site that need access to Workplace 365 or other applications that are connected to Microsoft Entra ID, Microsoft Entra Link cloud sync is the first solution to explore.
Setup and management are mostly carried out in the cloud, lessening your on-premises footprint. It supplies high availability and automatic failover, ensuring password resets and synchronization continue, even if there's a problem with on-premises servers. For complex, massive Microsoft Windows Server Active Directory to Azure advertisement Sync requirements such as integrating large groups (over 50,000 members), and device sync, use Microsoft Entra Link Sync.
Network Basics for High-Volume Workloads
However, they still require an existence on-premises in AD DS to access numerous resources. When an external user from a partner company is produced in Microsoft Entra ID using B2B, MIM can automatically provision them into advertisement DS and provide those visitors access to on-premises Windows-Integrated Authentication or Kerberos-based applications.
When a group is developed in Microsoft Entra ID, it can be immediately integrated to advertisement DS using Microsoft Entra Connect Sync. When users need access to cloud apps that still rely on legacy access procedures (for example, LDAP and Kerberos/NTLM), Microsoft Entra Domain Solutions synchronizes identities between Microsoft Entra ID and a managed Microsoft Windows Server Active Directory site domain.
After identities are in Microsoft Entra ID through HR-provisioning or Microsoft Entra Link cloud sync/ Microsoft Entra Link Sync, the employee can use the identity to access Teams, SharePoint, and Microsoft 365 applications. Workers still need access to lots of Microsoft applications to perform their work.
In addition to the pre-integrated gallery applications, Microsoft Entra ID supports provisioning to SCIM allowed line of company applications, whether hosted on-premises or in the cloud. The Microsoft Entra provisioning service develops users and groups in these applications, and handles updates such as when a user is promoted or leaves the company).