The Future of AI and CAPTCHA Solving
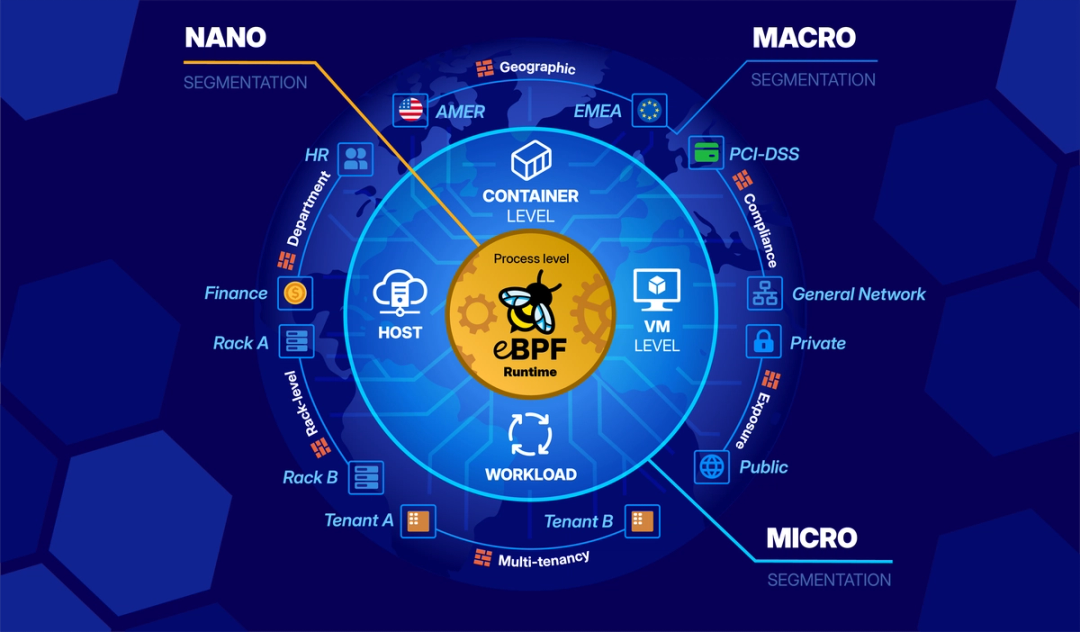
Network managers can put devices on various network segments, while they might also be geographically far-off. Security procedures needed differ depending on network configurations.
LAN networks can consist of various devices. A LAN could include computer systems, mobile phones, printers, IoT gadgets, tvs, and gaming consoles. Routers appoint IP addresses to all gadgets, which determine them on the network. Wide Location Networks are more common in contemporary company. They make up collections of LANs and cover large geographical locations.
The internet itself is specified as a WAN. Every ISP is likewise technically a WAN. Software-defined Wide area networks are laid over WAN networks. Agents on linked devices connect users to network resources. Managers can manage access via safe and secure entrances, and SD-WAN allows extensive traffic tracking. Business likewise tend to utilize SD-WAN to secure cloud properties efficiently.
The network layer is where data is sent. Servers develop packages of information, which they send to network gadgets via routing devices.
Future Cybersecurity Strategies: Access Management
Encryption conceals the contents of packets, protecting them versus external observers. Network devices are any items of hardware connected to the network architecture. Every network should be documented and mapped. Mapping makes it possible for managers to comprehend which devices require security. Company networks usually count on several gadget types: store info and software application.
- communicate details across the network. supplement the router and divert traffic efficiently. link network sections together. - connect to router devices and allow personnel protected access. link areas of the network with various protocols or security profiles. - guards network edges against malicious traffic. offer cordless gain access to for authorized devices.

It also examines the status of network gadgets such as servers or switches and notifies network managers when faults occur. Monitoring can be Proactive monitoring is preferable, expecting issues and seeking hazards before they trigger damage. Tracking can also be agent-based or agentless: This form of monitoring. Representatives connect to centralized tracking software.
High-Speed Server Hosting for Scale
This data might consist of memory usage and procedures running on the gadget. Agents might track user connections or examine general performance. Security teams should set aside time to update and log agents.
It involves package assessment to find details about information and network use. And it can also involve app tracking to guarantee only authenticated users have gain access to. Agentless tracking is non-intrusive and requires few resources. It offers an information stream that can be utilized to improve security setups. But this information is usually not granular.
Tracking is not always constant. Instead, security managers to assess functionality and security status. The gap in between security evaluations is the tracking period. Periods vary depending upon device type and circumstance. Service technicians set up constant examinations of the internal network. General network efficiency measurements may have longer monitoring intervals. This lowers the load positioned on the network.
It includes software application and hardware developed to find and obstruct malicious agents. Protecting networks likewise reaches gain access to control, network organization, and security policies. Networking security is. Cybersecurity guards versus digital dangers. InfoSec focuses on data defense. Both feed into securing a single computer connected to the network infrastructure versus outside dangers.
Comparing API-Based CAPTCHA Services Today
Companies depend upon reputable access to work and databases. However, they should protect confidential data from external observers by means of info security techniques. A well-thought-out security technique balances access and protection while likewise meeting compliance objectives. There are a number of networking security policy active ingredients. Common methods include: firewall softwares are the structure of the majority of security setups.
Access management gateways ensure just users with the proper qualifications can access network assets. Security policies specify access levels.
The code of apps can be susceptible to external attacks. Aggressors make use of vulnerabilities in app code to access network resources. Application security tests all apps and applies spots to upgrade code.